Exploiting Vulnerabilities at IXP Route Servers to Perform Stealth BGP Hijacks
Gabby Rimlinger , Joaquim Pereira , Matthieu Gouel , Olivier Fourmaux , Timur Friedman , Pedro de Botelho Marcos , Ronaldo A. Ferreira , Cristel Pelsser and Kevin Vermeulen
This 2026 international conference paper, by Gabby Rimlinger and 8 coauthors, was presented at ACM CCS 2026. Topics covered include networks, network security, bgp, hijacks, ixp, and path-hiding.
Full author list: Gabby Rimlinger, Joaquim Pereira, Matthieu Gouel, Olivier Fourmaux, Timur Friedman, Pedro de Botelho Marcos, Ronaldo A. Ferreira, Cristel Pelsser, and Kevin Vermeulen.
Abstract
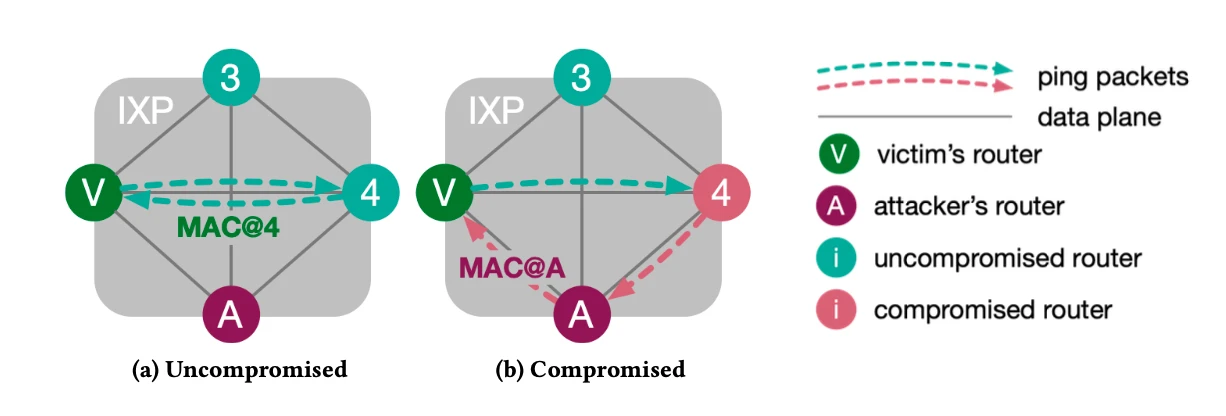
Internet Exchange Points (IXPs) are critical Internet infrastructure that interconnect tens of thousands of Autonomous Systems (ASes). To support scalable multilateral route exchange and fine-grained routing control, IXPs provide services such as route servers for scalable route dissemination and BGP communities for selective advertisement. Route servers enable both scalability and expressive routing policies, but some of their design choices can be exploited by a malicious actor. In this paper, we identify two of them: route-server path-hiding mitigation and the deployment of multiple independent route servers. Combined with well-known hijack techniques, these design choices allow an attacker to make multiple routes to the same prefix co-exist at the IXP, and strategically disseminate malicious routes to different subsets of peers, to increase their attack surface and the number of potentially vulnerable prefixes. We validate the feasibility of our attacks across three large IXPs, and show that these attacks increase the number of polluted ASes by 28% to 366%, and the number of vulnerable prefixes by 41% to 61%, depending on the IXP, compared to prior work. Moreover, we show that the IXP environment makes it easier to perform interception attacks than in other settings and allows such attacks to be invisible to public BGP collector peers. We also propose a novel data-plane detection technique based on the Layer-2 IXP architecture. Finally, drawing on discussions with IXP operators, we provide practical recommendations to improve route security and visibility at IXPs.
Publication Details
- Publication Type
- Conference Paper
- Publication Date
- November 2026
- Published In
- ACM CCS 2026
- Location
- The Hague, The Netherlands
- External Link
- https://hdl.handle.net/2078.5/280507
Suggested citation
Gabby Rimlinger, Joaquim Pereira, Matthieu Gouel, Olivier Fourmaux, Timur Friedman, Pedro de Botelho Marcos, Ronaldo A. Ferreira, Cristel Pelsser, and Kevin Vermeulen. 2026. Exploiting Vulnerabilities at IXP Route Servers to Perform Stealth BGP Hijacks. In ACM CCS 2026. The Hague, The Netherlands.
BibTeX Citation
BibTeX Citation
@inproceedings{Rimlinger2026,
	title        = {Exploiting Vulnerabilities at {IXP} Route Servers to Perform Stealth {BGP} Hijacks},
	author       = {Gabby Rimlinger and Joaquim Pereira and Matthieu Gouel and Olivier Fourmaux and Timur Friedman and Pedro de Botelho Marcos and Ronaldo A. Ferreira and Cristel Pelsser and Kevin Vermeulen},
	year         = 2026,
	month        = nov,
	booktitle    = {{ACM CCS} 2026},
	address      = {The Hague, The Netherlands},
	url          = {https://hdl.handle.net/2078.5/280507},
	abstract     = {Internet Exchange Points (IXPs) are critical Internet infrastructure that interconnect tens of thousands of Autonomous Systems (ASes). To support scalable multilateral route exchange and fine-grained routing control, IXPs provide services such as route servers for scalable route dissemination and BGP communities for selective advertisement. Route servers enable both scalability and expressive routing policies, but some of their design choices can be exploited by a malicious actor. In this paper, we identify two of them: route-server path-hiding mitigation and the deployment of multiple independent route servers. Combined with well-known hijack techniques, these design choices allow an attacker to make multiple routes to the same prefix co-exist at the IXP, and strategically disseminate malicious routes to different subsets of peers, to increase their attack surface and the number of potentially vulnerable prefixes. We validate the feasibility of our attacks across three large IXPs, and show that these attacks increase the number of polluted ASes by 28% to 366%, and the number of vulnerable prefixes by 41% to 61%, depending on the IXP, compared to prior work. Moreover, we show that the IXP environment makes it easier to perform interception attacks than in other settings and allows such attacks to be invisible to public BGP collector peers. We also propose a novel data-plane detection technique based on the Layer-2 IXP architecture. Finally, drawing on discussions with IXP operators, we provide practical recommendations to improve route security and visibility at IXPs.},
	groups       = {International Conferences},
	keywords     = {Networks, Network security, BGP, Hijacks, IXP, path-hiding}
}
Related publications
A Taxonomy of Attacks Using BGP Blackholing
Loïc Miller and Cristel Pelsser
European Symposium on Research in Computer Security, 2019
Measuring the Impact of RPKI on the BGP Updates Volume
Samuele Quinzi, Cristel Pelsser, and Giuseppe Di Battista
Proceedings of the ACM on Networking, 2026
The Next Generation of BGP Data Collection Platforms
Thomas Alfroy, Thomas Holterbach, and Thomas Krenc, et al.
Proceedings of the ACM SIGCOMM 2024 Conference, 2024
Internet Science Moonshot: Expanding BGP Data Horizons
Thomas Alfroy, Thomas Holterbach, and Thomas Krenc, et al.
Proceedings of the 22nd ACM Workshop on Hot Topics in Networks HotNets, 2023